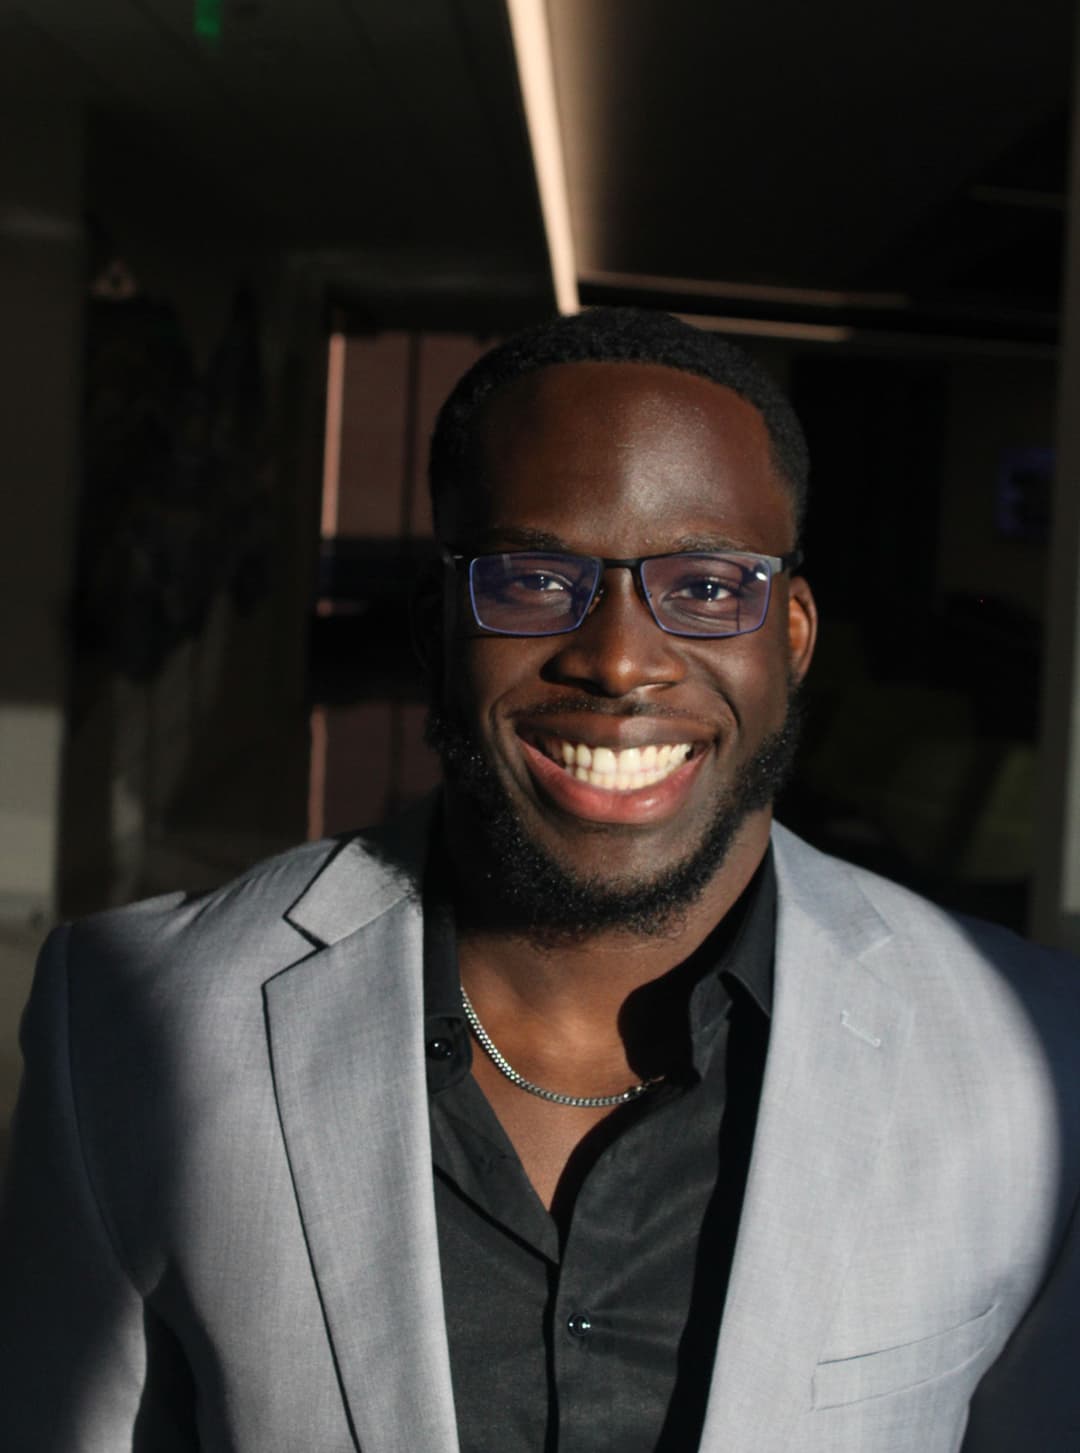
Founder

Justin Duru

Founder and Lead Security Consultant, PurveX

I help security teams make sure their alerts actually fire, and I train the analysts who will run them.

Justin Duru
  • BackgroundSOC analyst to security instructor
  • Core toolsMicrosoft Sentinel, Splunk SOAR
  • CertificationsCySA+, Security+
  • Teaching atEllington Cyber Academy

My story

I lead by serving the work, not standing above it.
  1. 1
    Where I started

    Before this was a company it was three jobs: tuning Microsoft Sentinel for a federal agency, automating response in Splunk SOAR, and teaching SOC fundamentals at Ellington Cyber Academy. All three taught the same lesson. Real growth comes from hands-on repetition, not from watching someone else do the work.

  2. 2
    What actually matters

    Hands-on work is not enough once AI can write the query and summarize the alert. What still matters is knowing how to think: how to read what a system is telling you, when to trust it, and when to push back. That judgment is what I teach, instead of a shortcut to a flag.

  3. 3
    Why PurveX exists

    I kept running into two gaps. Smaller security teams need stronger coverage and do not have the headcount to build and maintain it by hand. And new analysts finish their training knowing the terms but not the work, because they never practiced on a real network. PurveX takes on both. AI agents can close the coverage gap when they are paired with someone who understands what is happening underneath, and hands-on training builds the analysts who will be that someone. No team should need to be enterprise-sized to be secure.

Consulting

Hands-on help with your SIEM and detections

I find the alerts that would miss a real attack, then fix them before one happens.

What is going wrong on your team?

The fix

Detection engineering

Your SIEM runs vendor rules that were never written for your logs, so real attacks slip past without an alert.

What's included
  • Review the logs you already collect
  • Write rules mapped to MITRE ATT&CK techniques
  • Test each rule against real attack behavior before handing it over
You getTested detections, ready to run in your SIEMBook a call
How it works
  1. 1Book 30 minutes

    Tell me about your SIEM, your team, and what worries you.

  2. 2Review together

    We look at what fires, what does not, and where the gaps are.

  3. 3Agree a scope

    A short, focused engagement with a clear result.

Let's talk

Thirty minutes about your SIEM, your team, or your training program.

Hold30 min
Open conversation